Prepare your SOC 2 report from your existing security assessment
US customers frequently request a SOC 2 report when evaluating their vendors. Komplyo covers the Trust Services Criteria from your existing security assessment, isolates the missing COSO governance controls, and measures your readiness continuously up to the observation window.
Who needs a SOC 2 report?
SOC 2 is not a legal obligation: it's a trust standard that has become unavoidable in certain B2B sales:
SaaS selling into the US
The SOC 2 report is the standard artifact of American security due diligence. Often a hard gate in procurement, whatever the vendor's size.
Scale-ups going enterprise
Large accounts, including European ones, often accept SOC 2 as an alternative or complement to ISO 27001 when qualifying SaaS vendors.
Type 1 or Type 2
Type 1 attests control design at a point in time; Type 2 their operation over an observation period (3 to 12 months). Demanding customers ask for Type 2.
What a SOC 2 report covers
The audit evaluates your controls against the AICPA's Trust Services Criteria (TSC):
Security (common criteria, CC)
The mandatory core of every report: COSO governance, risk management, access controls, operations, change management.
Availability, Confidentiality, Processing Integrity
Optional categories, activated per your contractual commitments: service availability, protection of confidential information, processing integrity.
Privacy
The personal-data category. For a European company it overlaps very largely with GDPR, already covered by your Komplyo module.
COSO governance controls
Ethics, board oversight, organisational structure, competence: criteria that cannot be derived from technology and need their own evidence.
Evidence across the observation window
For a Type 2, each control must produce regular evidence throughout the audit window. Tooling and discipline matter as much as policies.
30 of 38 criteria already covered by your assessment
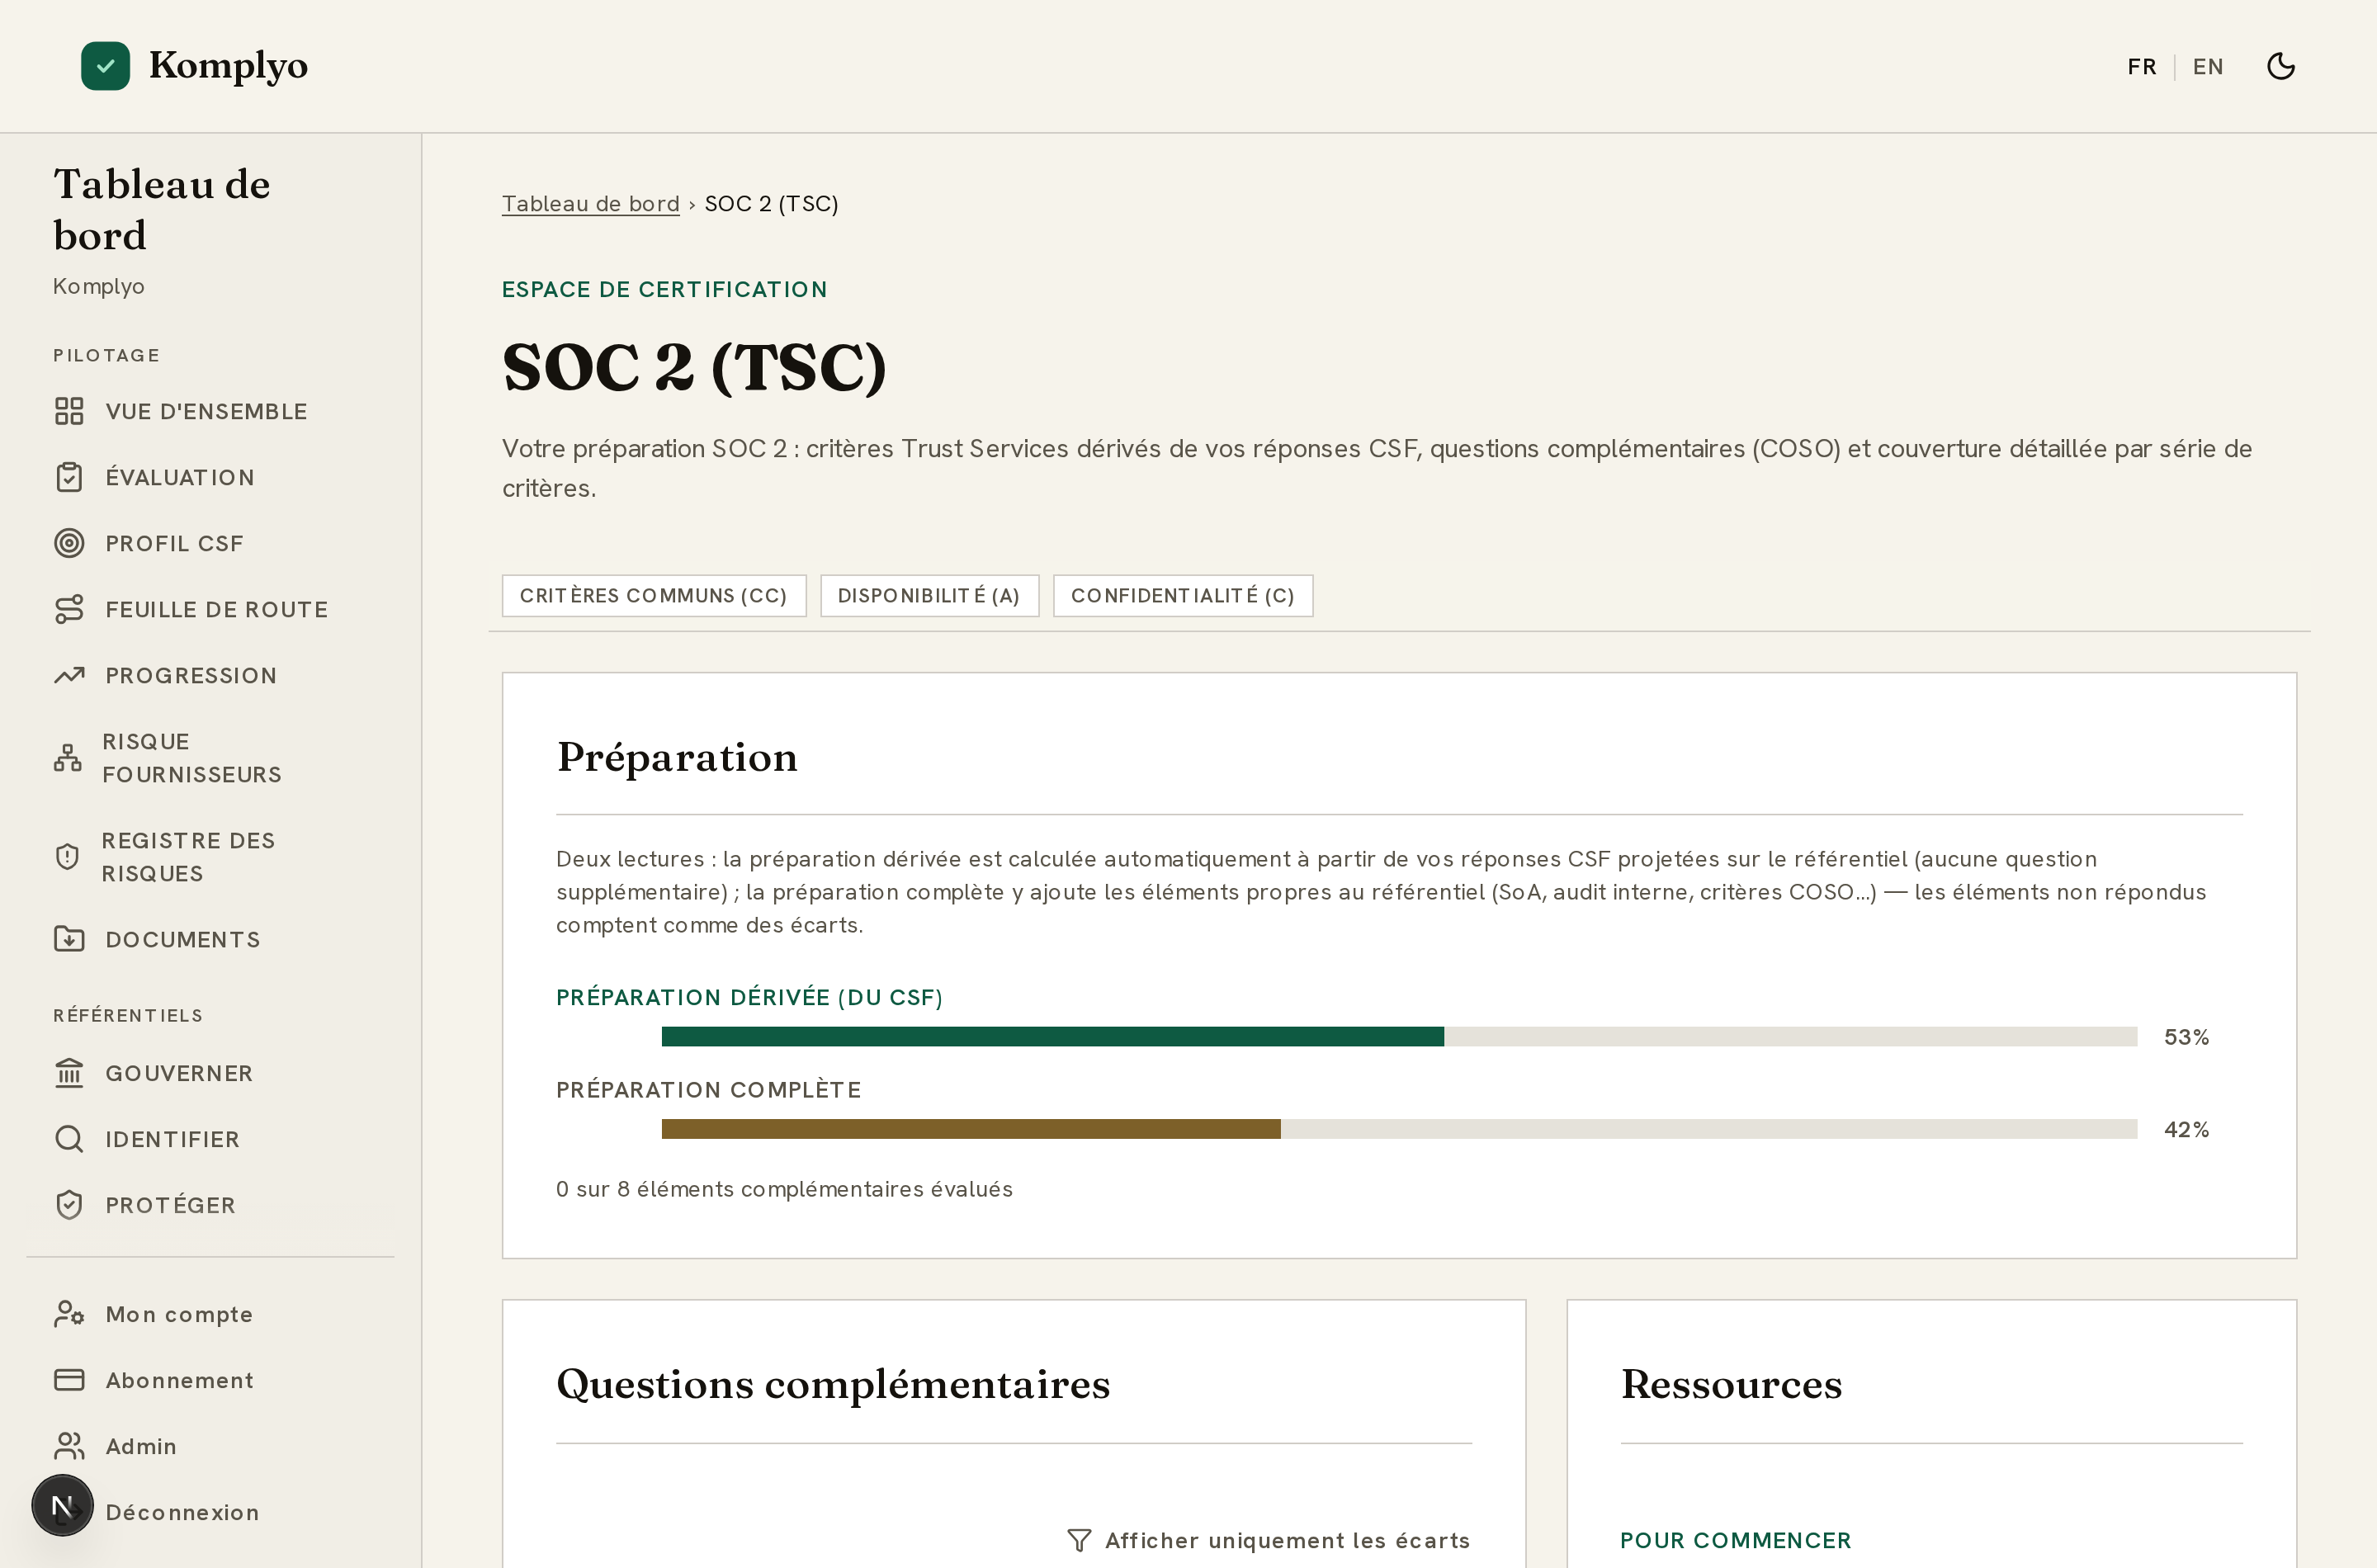
Komplyo derives 30 of the 38 TSC criteria from your NIST CSF 2.0 assessment via its mapping table, and isolates the 8 COSO governance criteria that require their own answers. The Privacy category reuses your GDPR module. Nothing is assessed twice.
- A dedicated SOC 2 workspace. Every TSC criterion with its coverage status, series by series (CC, A, C, PI, P).
- Derived then comprehensive readiness, stored over time. You track progress until you're audit-ready.
- Generated policies and registers. The documentation base the audit firm will request in the very first call.
Your SOC 2 preparation deliverables
Everything you need to enter scoping with the audit firm from a position of strength:
- TSC criteria coverage map (series by series)
- Security policies aligned with the common criteria
- Risk register and treatment tracking
- Prioritised roadmap up to the observation window
- Readiness history. Also useful to reassure prospects before the report exists
Further reading
Our practical guides on the topic:
Your first risk register: a proportionate method aligned with EBIOS RM and ISO 27005
Risk registers for SMEs: what ISO 27001 (clauses 6.1.2 and 8.2) and NIS2 require, how to start with EBIOS RM workshop 1 (scoping and security baseline), which columns to keep and which pitfalls to avoid. An iterative method aligned with ISO/IEC 27005:2022.
Answering a customer security questionnaire without losing a week: a method for SMBs
CAIQ, SIG, 200-row custom spreadsheets: customer security questionnaires have become a fixture of B2B sales. A 5-step method for SMBs: one answer base aligned with NIST CSF 2.0, projection into each framework's vocabulary, and evidence ready before it's requested.
30 compliance documents from a single assessment: how it works
Security policy, ISO 27001 SoA, risk register, business continuity plan, DPIA, records of processing, NIS2 scope memo… How one assessment aligned on NIST CSF 2.0 generates 30+ deliverables ready for your customers and auditors.
NIST CSF 2.0 for SMEs: the six functions and how to implement them
The NIST Cybersecurity Framework 2.0 organizes cyber risk management into six functions: Govern, Identify, Protect, Detect, Respond, Recover. What each function expects from an SME, category by category, and a 90-day implementation sequence based on the NIST SP 1300 guide.
Business Impact Analysis for SMBs: a five-step method
A Business Impact Analysis (BIA) prioritizes assets by business criticality rather than technical value. A five-step method for SMBs, based on NIST SP 800-34, NIST CSF 2.0, CISA resources and ANSSI's EBIOS Risk Manager.
SOC 2. Frequently asked questions
Type 1 or Type 2. Where should we start?
Type 1 (control design at a point in time) is faster to obtain and satisfies some customers' requirements; Type 2 (operation over 3 to 12 months) is what demanding customers expect. Many companies do a Type 1 then roll straight into the Type 2 observation window.
Who issues the SOC 2 report?
Only a licensed CPA firm, after an audit. Komplyo doesn't issue the report: it prepares your controls, documentation and readiness so the audit holds no surprises.
How long does SOC 2 preparation take?
Expect 2 to 4 months of control preparation, then the observation window (3 to 12 months) for a Type 2. Starting from your existing security posture (which is what Komplyo does) significantly shortens the first phase.
Is SOC 2 recognised in Europe?
Yes, especially among large accounts and technology companies. But if your customers are mostly European, ISO 27001 is often better recognised. With Komplyo, the same assessment prepares both.
Do we have to cover all five TSC categories?
No. Only Security (the common criteria) is mandatory; Availability, Confidentiality, Processing Integrity and Privacy are added per your contractual commitments. A first report is often Security + Availability.
We're GDPR-compliant. Does that help with Privacy?
A lot. The TSC Privacy category overlaps largely with GDPR: in Komplyo it is fed directly by your GDPR module, with no additional questionnaire.
Measure your SOC 2 readiness today
Create your workspace, activate the SOC 2 lens and see immediately what's covered and what's missing.